Automate Firewall Change Requests
Resolve takes every firewall request from ITSM ticket to verified push and closes the change record on its own.

Firewall Change Requests Outpace the Engineers Who Can Push Them.
Tired of watching a release slip two days because one port 443 request is stuck in the network queue behind a hundred others?
Your engineers check the rule base, push the change by hand, update the spreadsheet, and circle back to close the ticket, and 12% of large enterprises run that loop more than 1,300 times a week.
Resolve takes that loop off your plate the moment a request lands. It validates against policy, routes the approval, pushes the change, verifies the traffic path, and closes the record with the evidence attached, so your releases ship on the date you promised.

Ship Rule Changes at the Pace of the Release
Validation, approval, push, and change record run in one workflow, so releases move at the pace of the request.

Pass Every Audit With the Evidence Attached
Every rule carries its ticket, approver, check results, and rollback plan, so audit prep becomes a report you pull in minutes.

Network Engineering as a Strategic Function
With routine rule requests running on their own, your engineers spend their week on valuable initiatives to move the business forward.
Firewall Automation That Checks Before It Changes
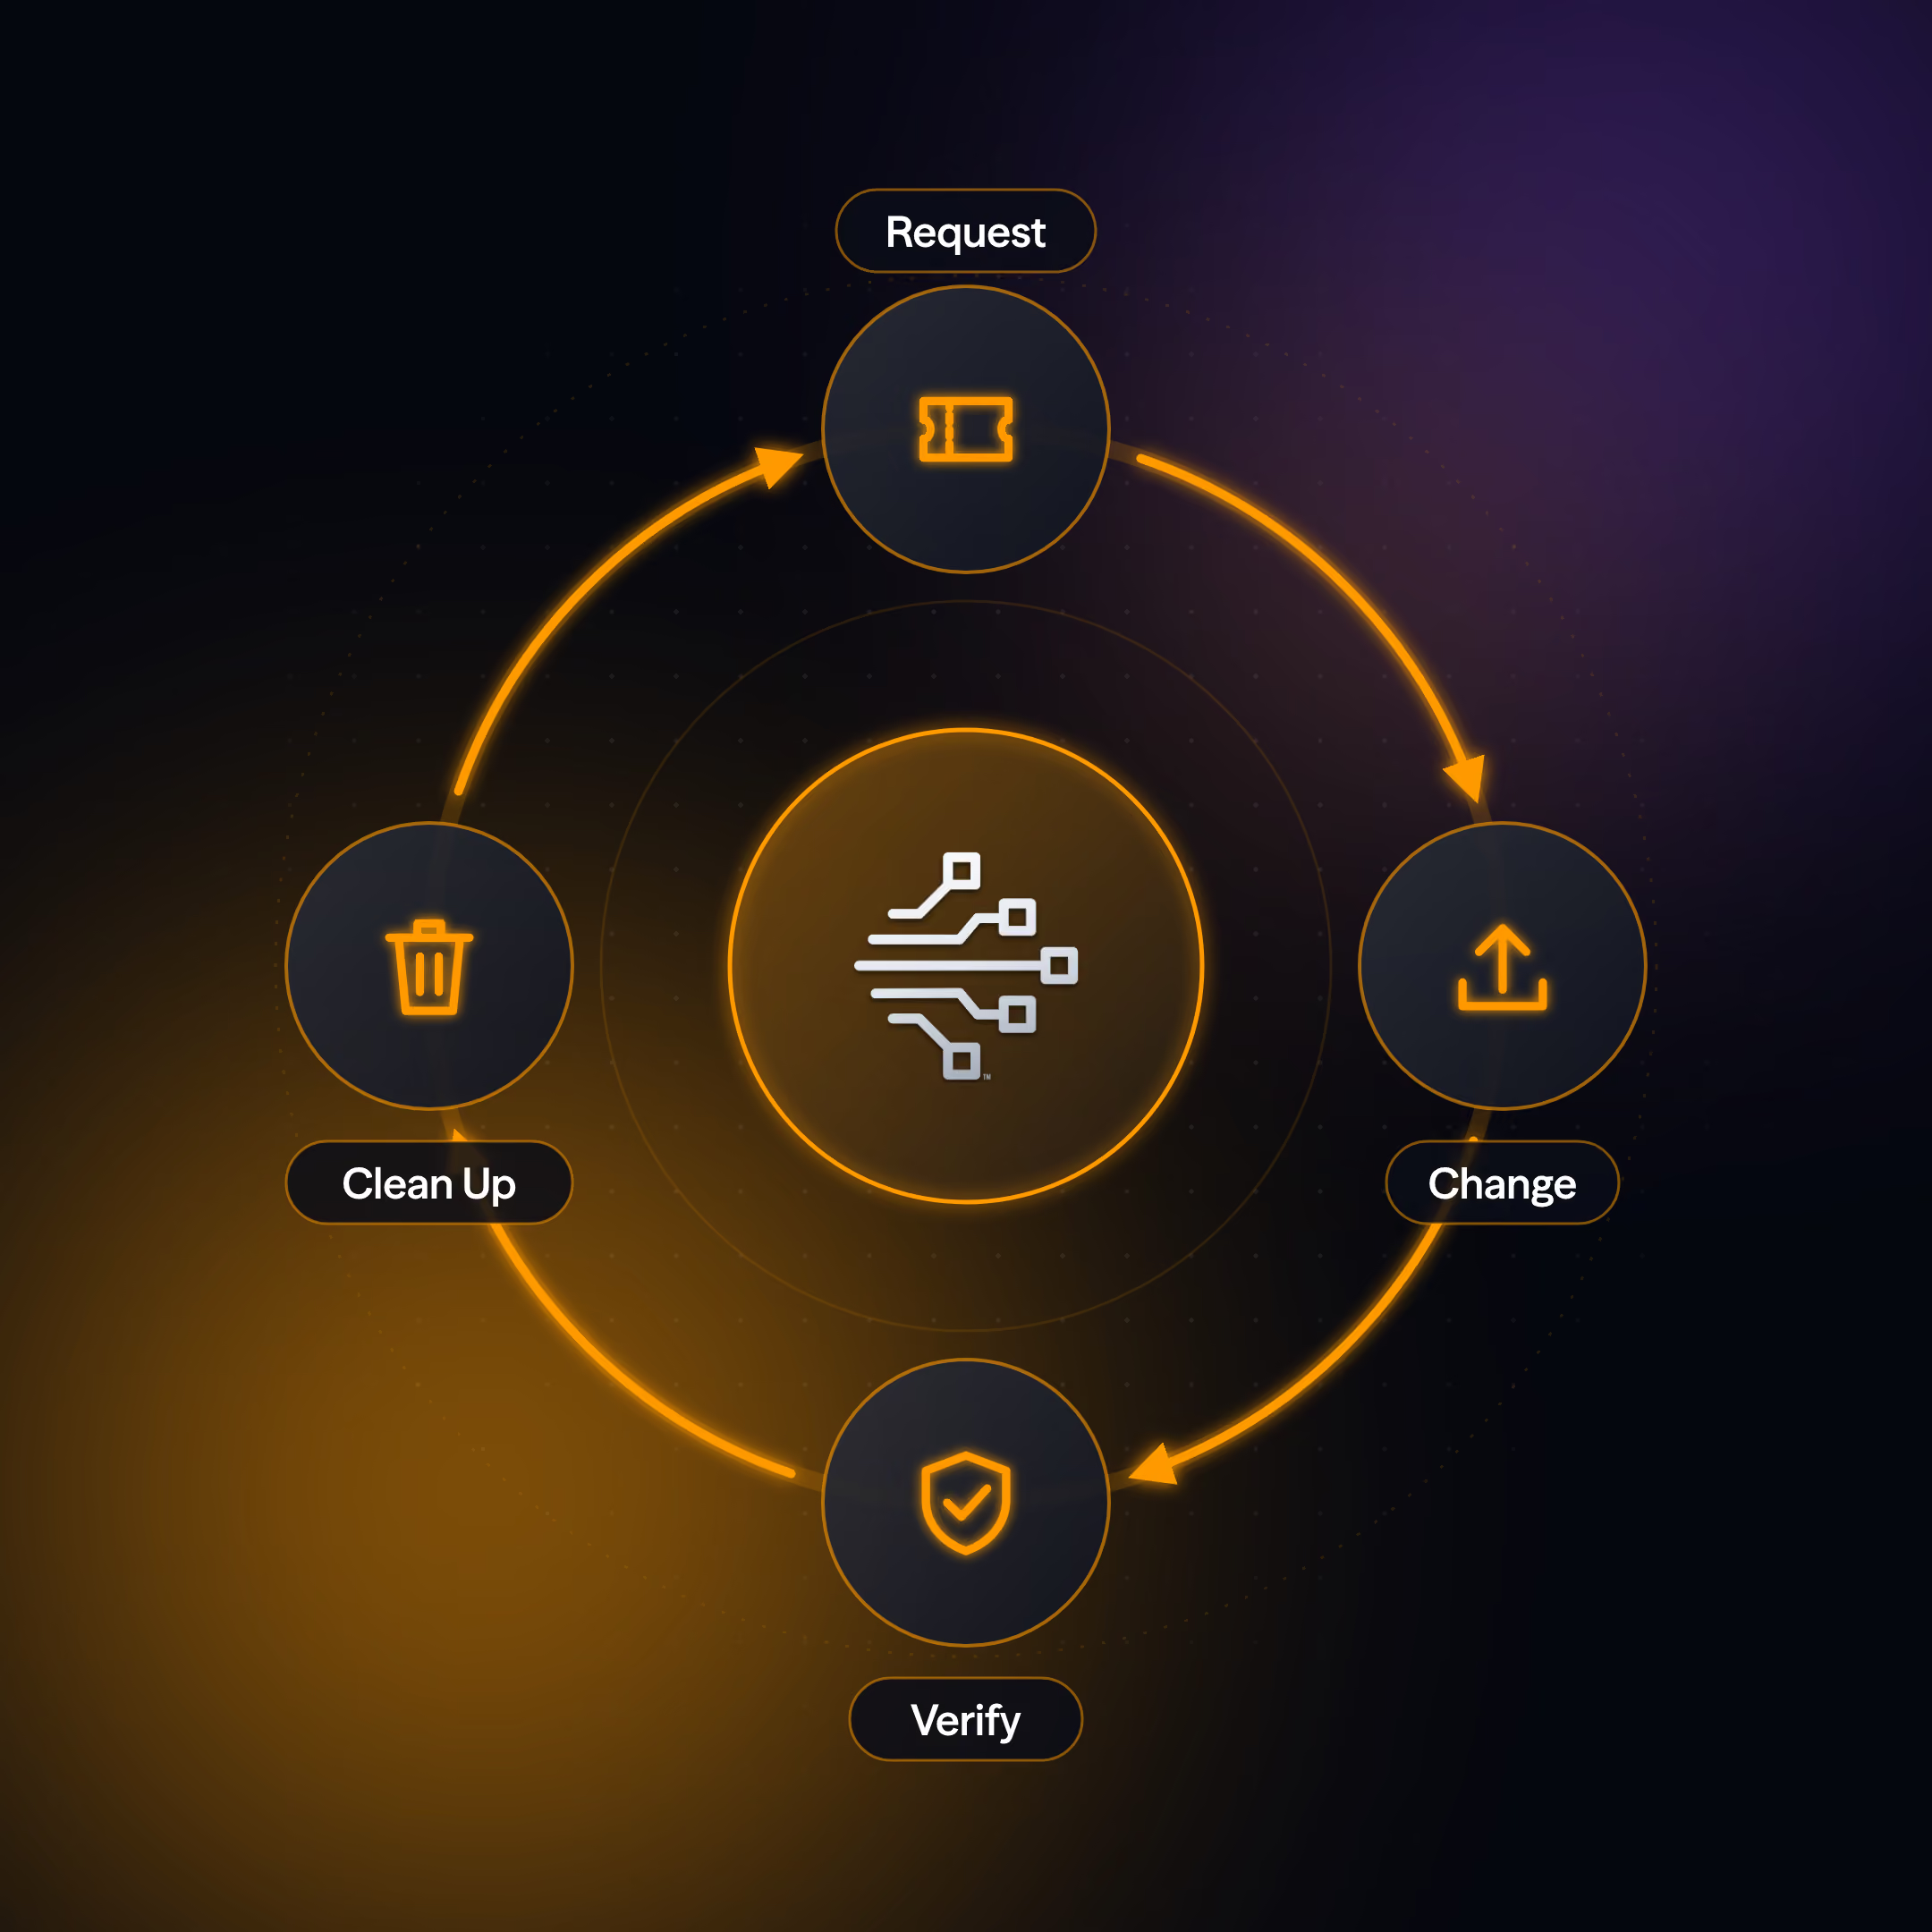
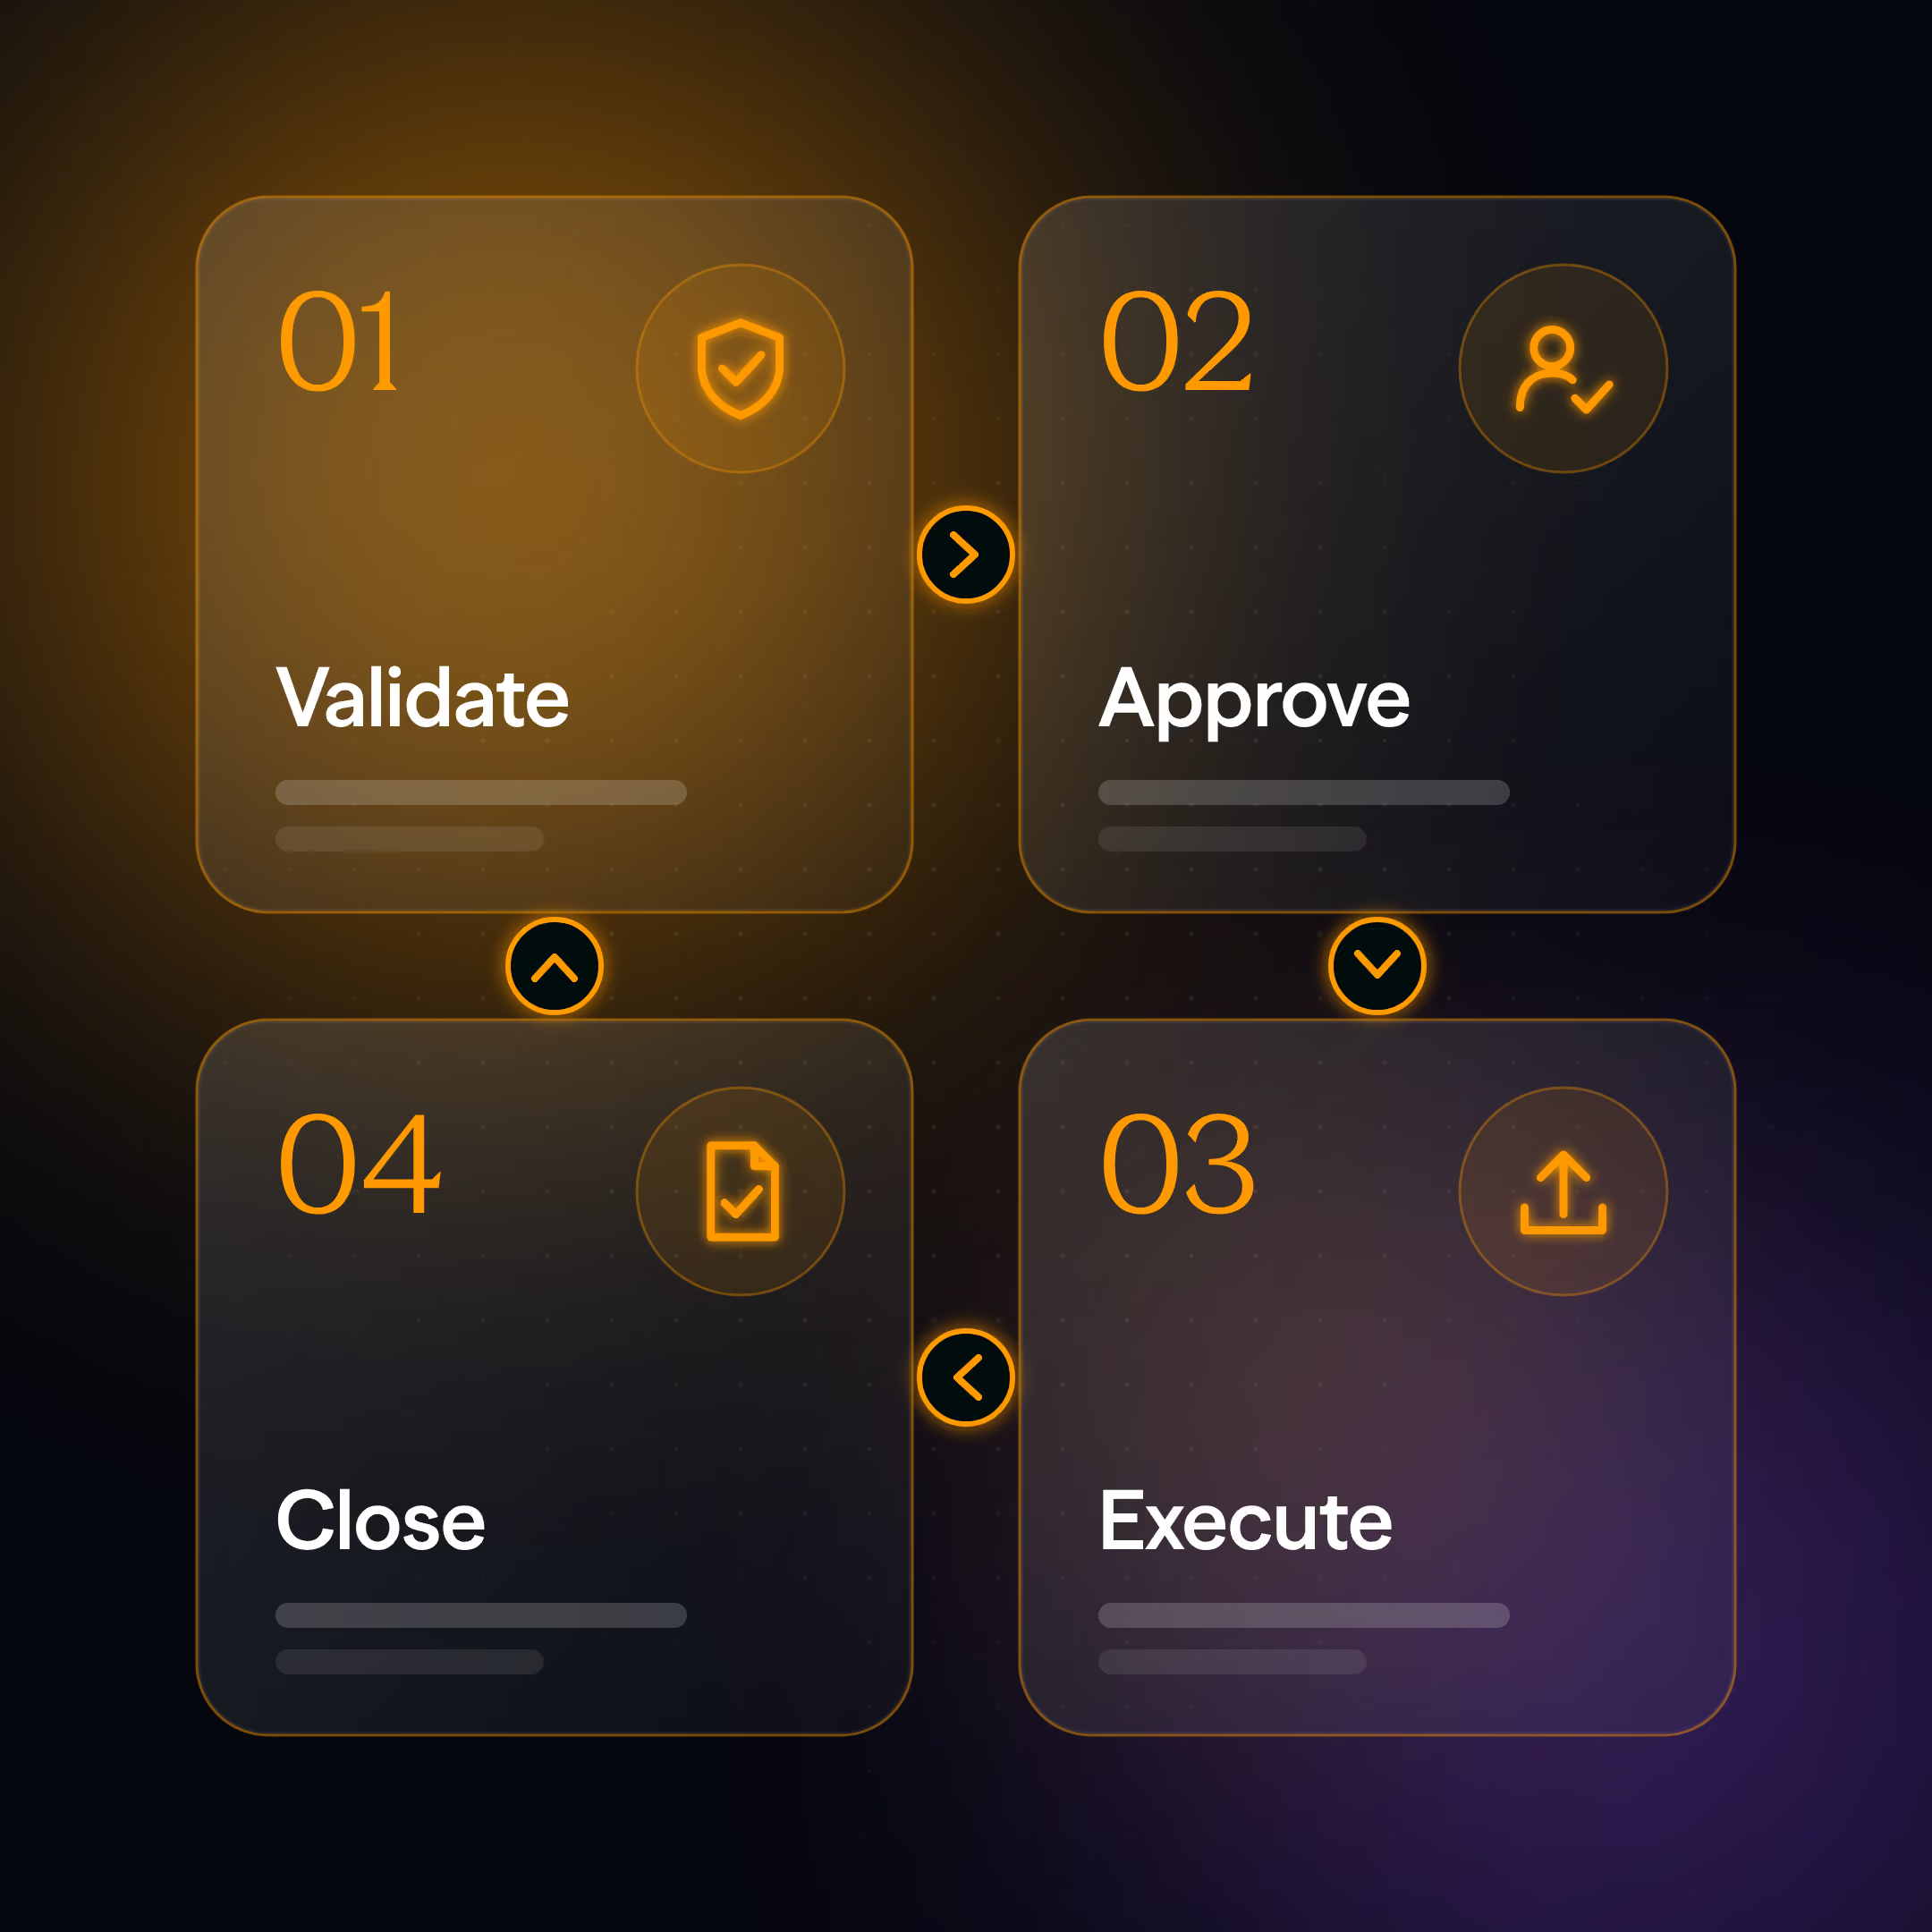
The moment a rule request lands in ServiceNow, Jira, the portal, or chat, Resolve runs a four-step loop from ticket to verified change.
1. Validates the request against policy and the live rule base, flagging duplicates and conflicts before approval.
2. Routes approval to the right owner or change board with the pre-check results attached.
3. Pushes the change, verifies the traffic path, and rolls back automatically if a check fails.
4. Closes the change record with the evidence attached and updates the CMDB.
Transform How Your Network Team Handles Firewall Changes
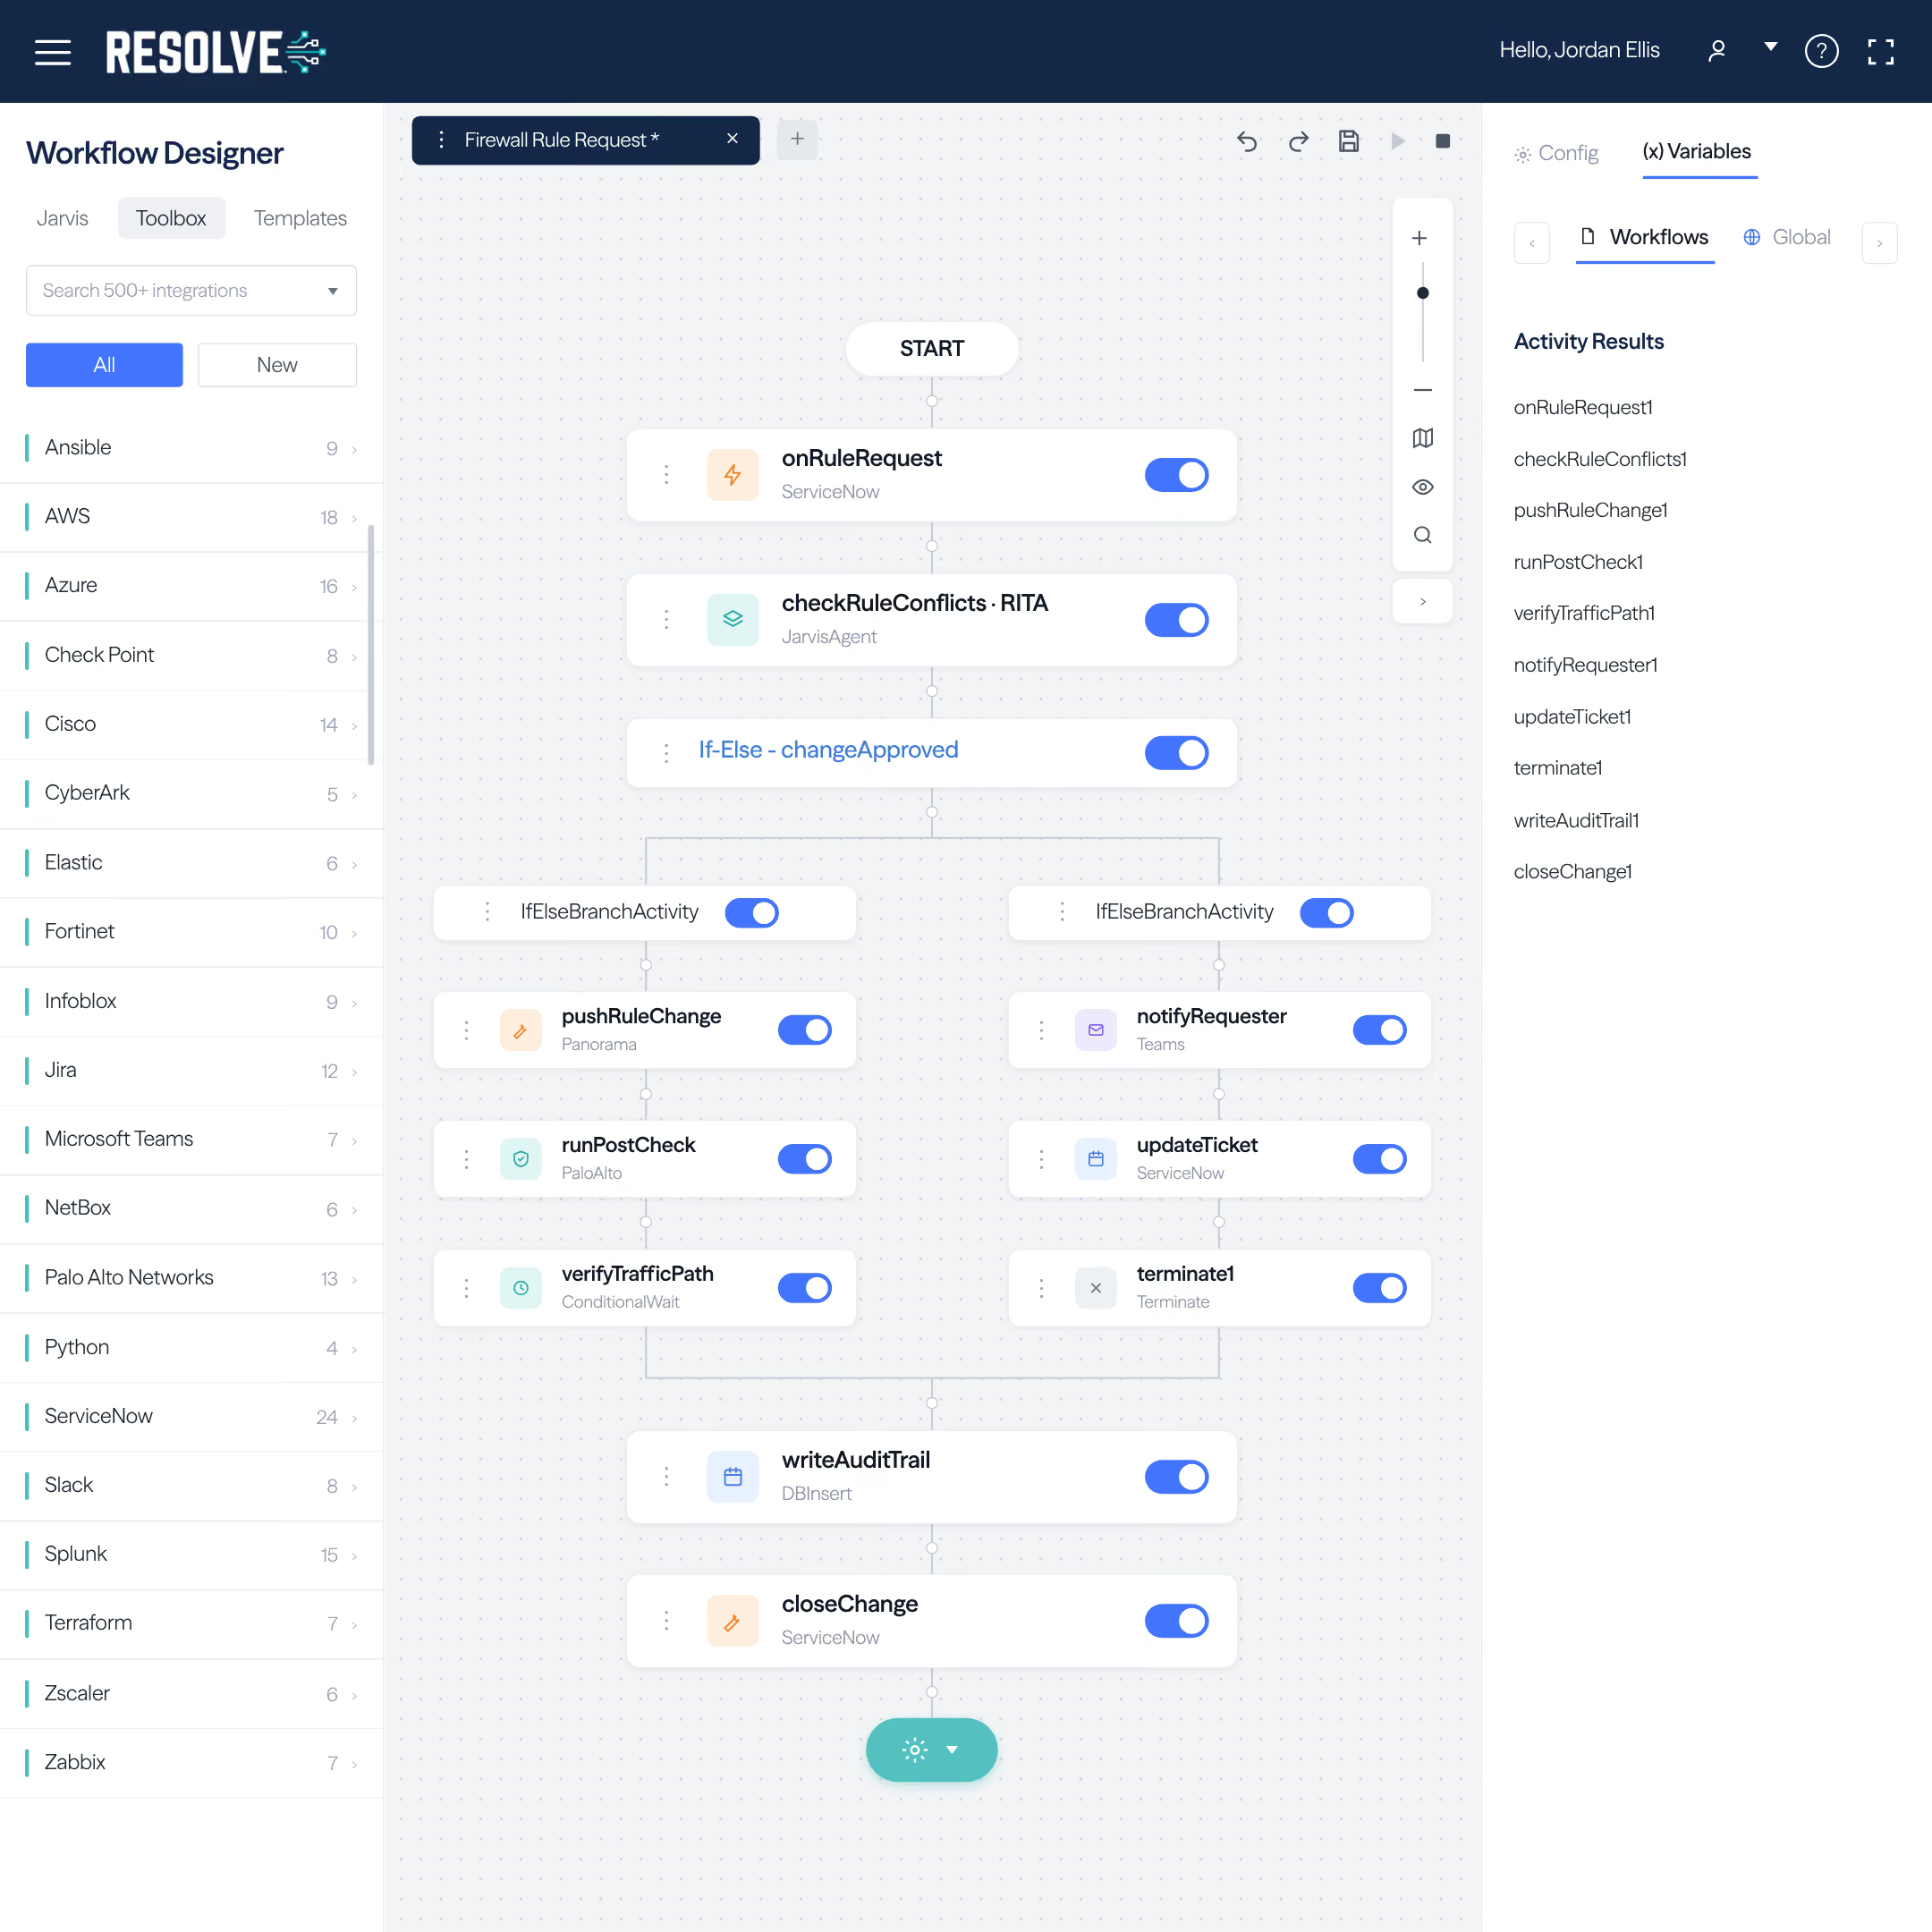
Resolve executes every rule request through the tools your network team already trusts, with no swivel-chairing between the ticket and the firewall console.
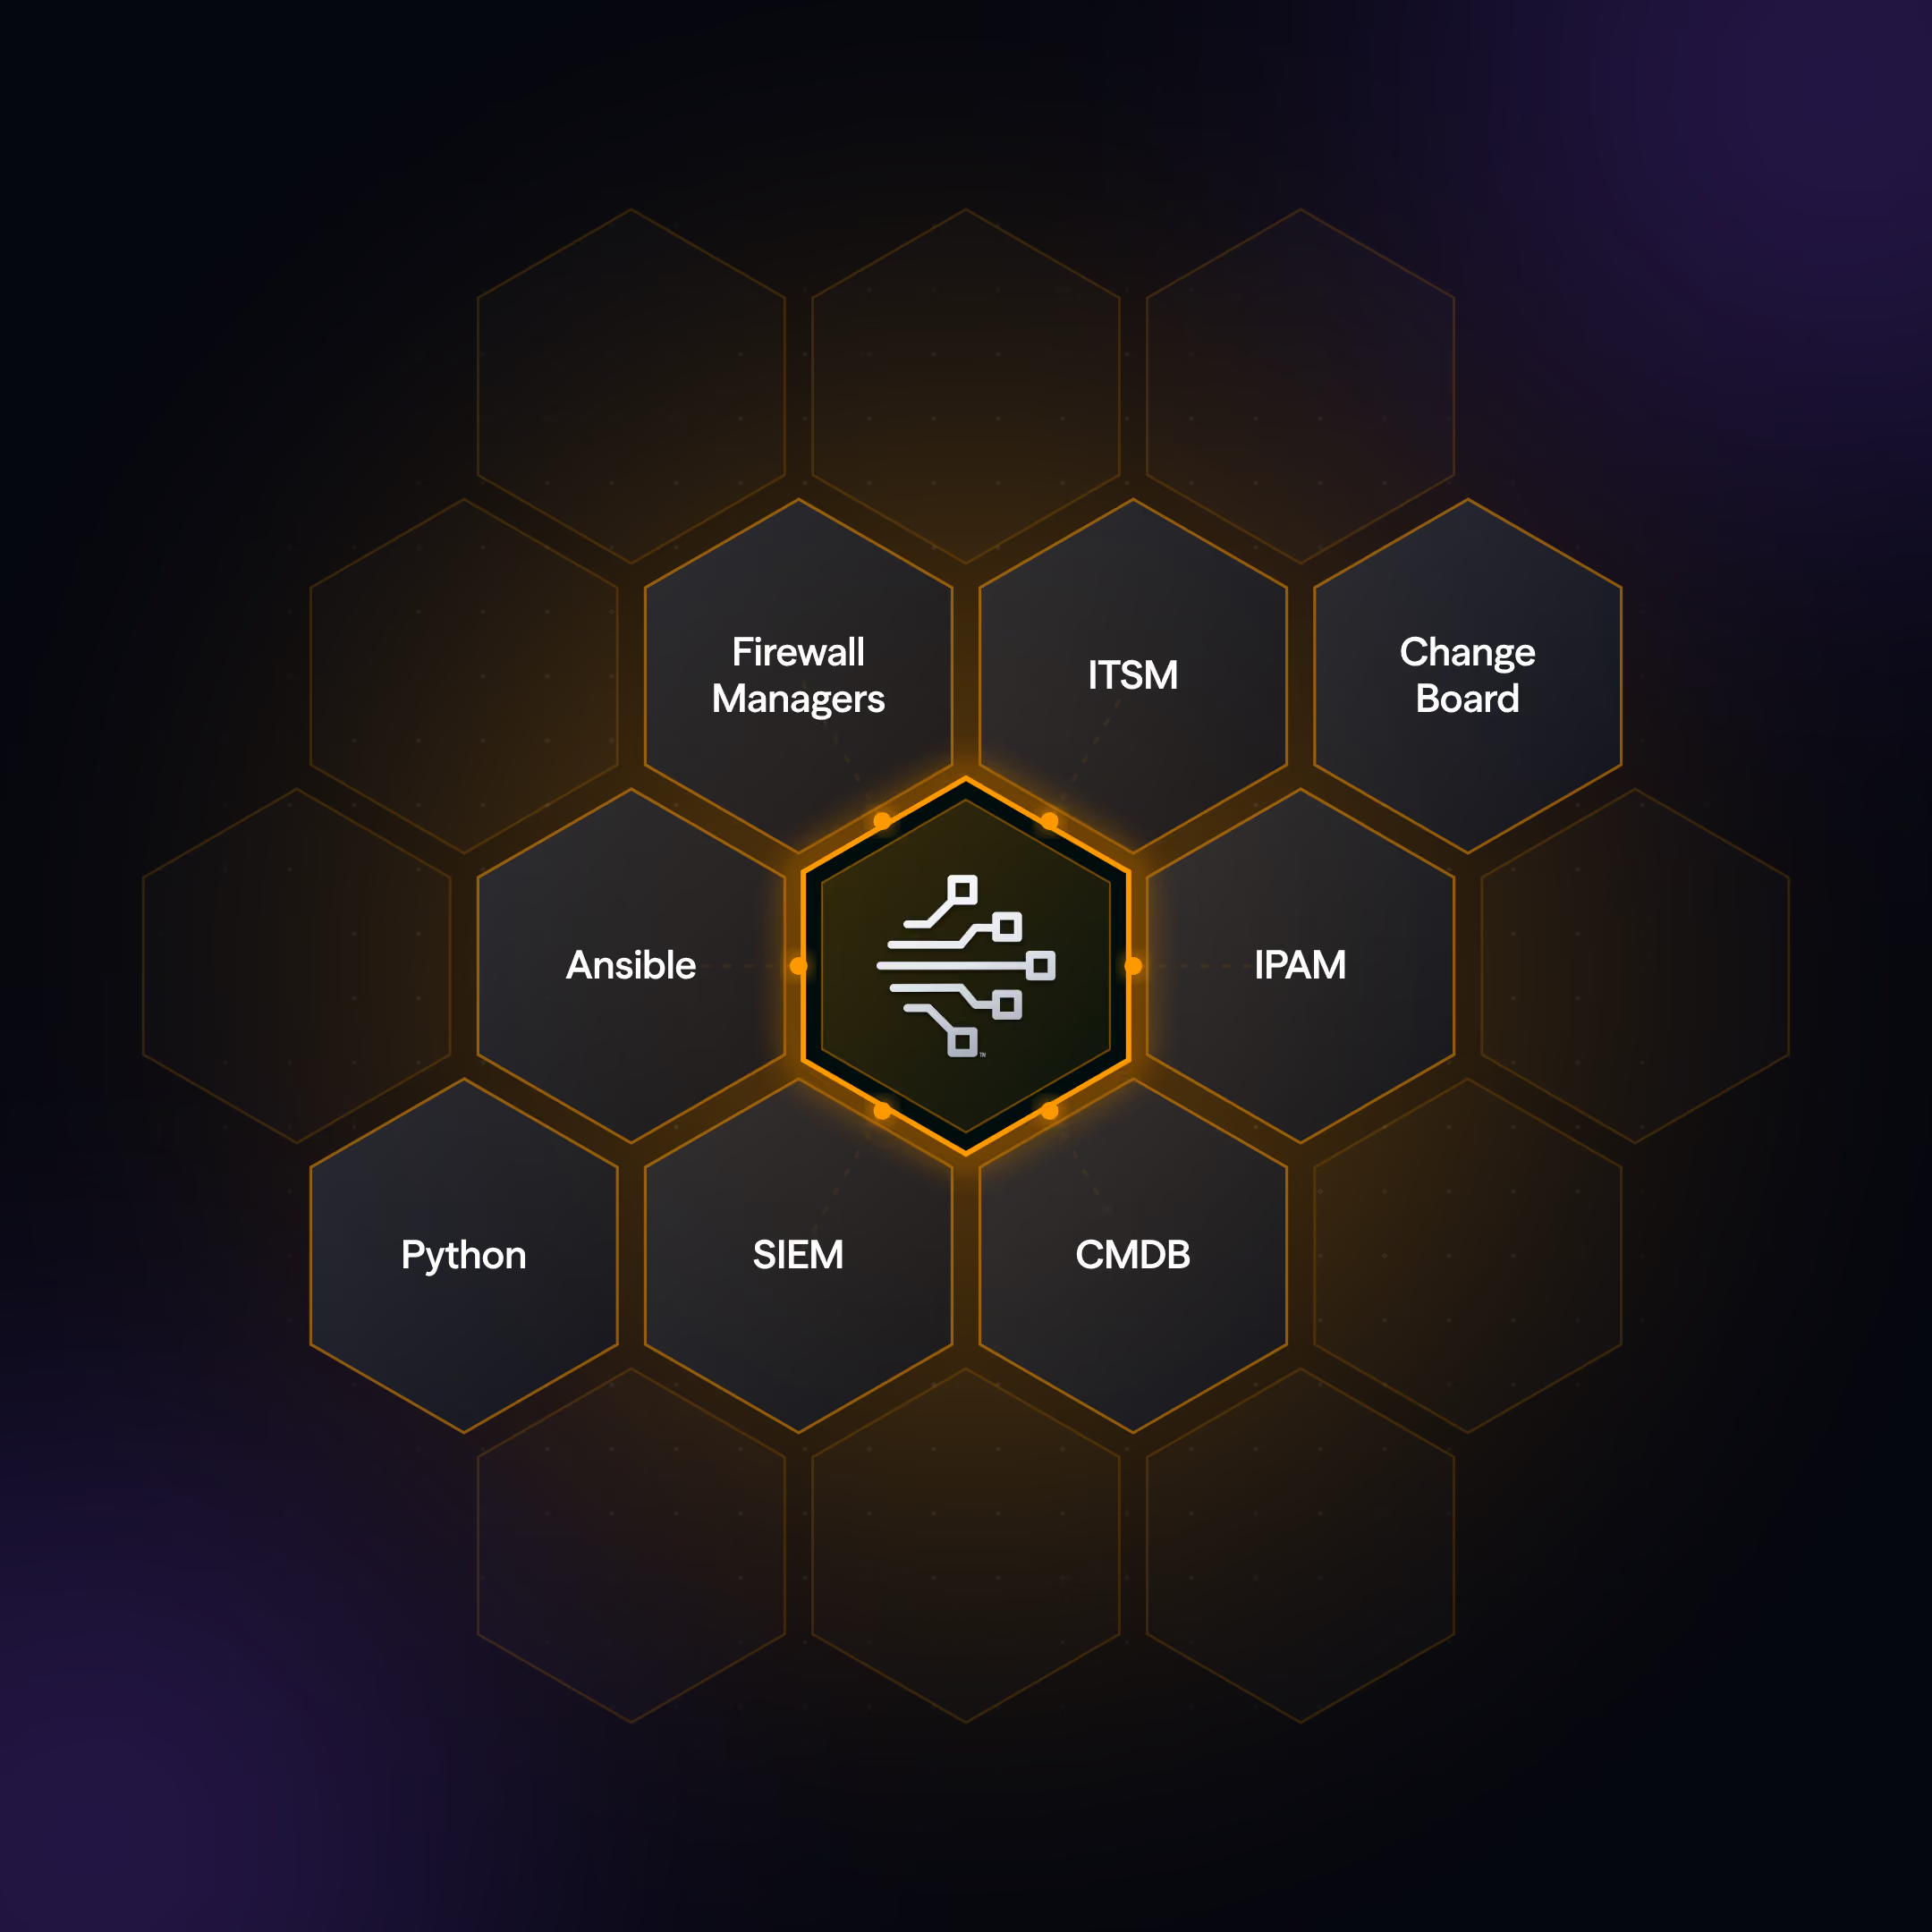
Firewall Change Automation Built on Your Existing Stack. Runs across Palo Alto Networks, Fortinet, Check Point, and Cisco, plus the ITSM, IPAM, and CMDB systems behind every change.
Policy-Aware Pre-Checks. Conflicts, duplicates, and overly broad rules surface before approval.
Governed Approvals. Every change reaches the right owner with full context and separation of duties enforced.
Verified Execution and Rollback. Every push is verified, and failed checks roll back automatically.
Low-Code That Runs Your Code. Build visually and drop in your own Python, Ansible, or vendor API calls anywhere in the flow.
Prebuilt Firewall Workflows. Start from ready-made rule request, object update, and decommission workflows.
Built for the Network Team, Connected to Everything Else
Firewall change automation runs on Resolve's Agentic Resolution Fabric, so every rule change becomes one governed step in a larger infrastructure workflow.
Approvals, role-based permissions, and a complete audit trail ride on every change, with each push mapped to its ticket and approver.
500+ native integrations across firewalls, controllers, ITSM, IPAM, CMDB, and SIEM, and your existing scripts and playbooks plug straight in.
Change outcomes and failed checks surface automatically, stale rules get flagged for cleanup, and every repeat request runs faster.
What Changes When Every Firewall Change Request Runs Through Resolve
Every rule request follows the same governed path, so your network team gains speed, consistency, and audit confidence with every change it ships.
Rule requests move from ticket to verified push in one workflow, with no queue time between handoffs.
The same validation, approval, and verification steps run on every change across every firewall vendor.
Every rule carries its ticket, approver, check results, and rollback plan the moment it ships.
Pre-checks catch conflicts before approval, and automatic rollback contains anything that slips through.
Stale and redundant rules get flagged for cleanup, so the rule base stays lean as the business grows.